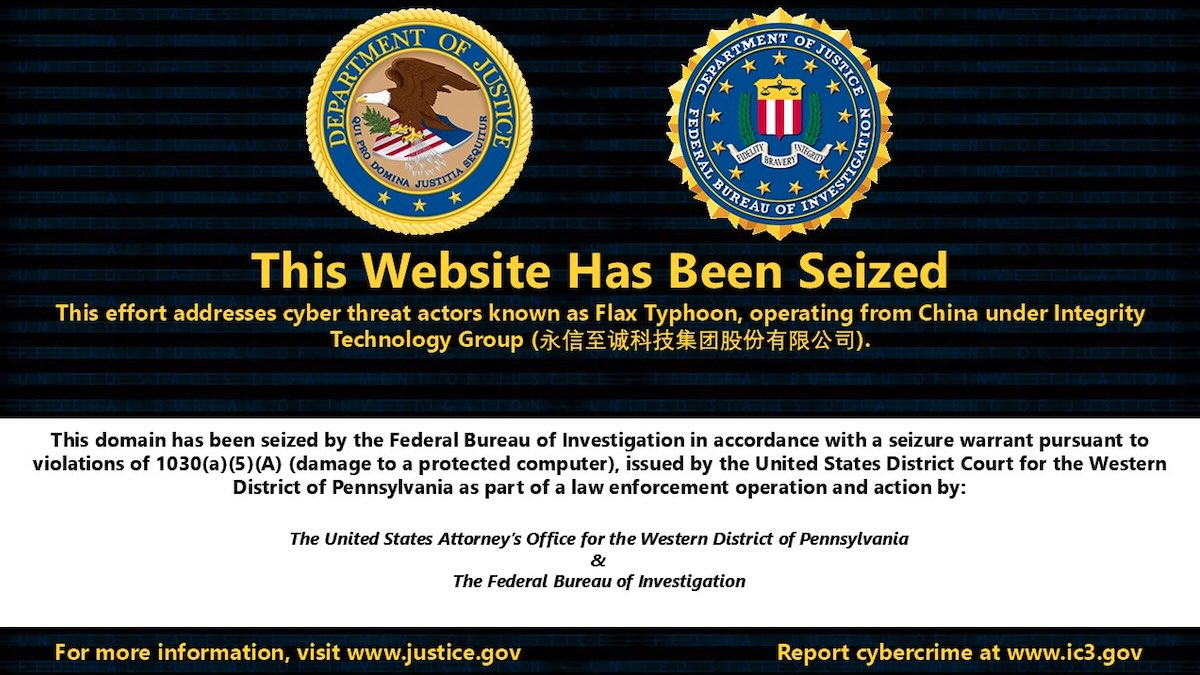
US Disrupts Chinese Hacking Tools MicroScan and FishHub
The United States announced on Thursday the disruption of two hacking tools used by Chinese state-sponsored threat actors in attacks against US and foreign critical infrastructure. The tools, MicroScan and FishHub, were developed by Integrity Technology Group (Integrity Tech), a company linked to Chinese state-sponsored advanced persistent threat (APT) groups.
MicroScan has been used for vulnerability scanning, while FishHub enabled network intrusions through spear phishing campaigns. According to US authorities, Integrity Tech employed a variant of the Mirai malware to build an Internet of Things (IoT) botnet that facilitated MicroScan’s use for reconnaissance against victim networks.
This reconnaissance activity targeted a range of organizations, including a US power company, non-governmental organizations (NGOs), airports in Japan and Poland, and critical infrastructure entities and universities in Taiwan.
FishHub allowed Integrity Tech’s clients to gain remote access to victim networks, search for specific files, and exfiltrate data. The tool has been specifically linked to attacks against at least 20 universities in Taiwan.
As part of the disruption, the US seized multiple domains used by the threat actors to access MicroScan and FishHub. These domains include c0cc[.]cc, 98aicai[.]com, 98aicode[.]com, outlook3650[.]com, youtubecard[.]com, and linkedinns[.]net.
This action follows prior US efforts against Integrity Tech. In 2024, the United States disrupted the company’s Raptor Train botnet. In 2025, the US sanctioned Integrity Tech for providing cybersecurity products to Chinese state-sponsored APTs, including Flax Typhoon. The European Union later sanctioned the company in March 2026.
Joint Advisory Reveals MicroScan’s Long-Term Use and Technical Details
A new joint advisory, issued by government agencies from the United States, United Kingdom, Australia, Canada, Japan, New Zealand, and Spain, confirms that MicroScan has been active since at least 2017. The advisory describes MicroScan as a Python-based web application containing over 1,300 penetration testing scripts designed to scan websites for specific vulnerabilities.
The tool has been primarily associated with Flax Typhoon, also known by aliases such as Ethereal Panda, Red Juliett, Storm-0919, and UNC5007. However, the advisory notes that Integrity Tech is believed to have worked with other Chinese APT groups beyond Flax Typhoon.
Flax Typhoon has been observed using a variety of reconnaissance tools alongside MicroScan, including BBScan, dirsearch, Fscan, ksubdomain, masscan, Nmap, OneForAll, ShuiZe, and WPScan. For initial access, the group has employed command-line exploit utilities and the EBurst Microsoft Exchange password spraying tool.
To maintain persistence within compromised networks, threat actors have deployed virtual private network (VPN) tools such as SoftEther. For data exfiltration, they have used the PHP script Curlc4.txt, the command-line utility office-cli to extract email data, and DC.ex to harvest sensitive information from Active Directory.
Advisory Details Email Data Theft and Geographic Restrictions
The joint advisory states that threat actors collect account credentials and exfiltrate victim email data from both on-premises systems and cloud-based services. Observed victims of email data theft include government organizations, law enforcement agencies, healthcare systems, and religious institutions located in Southeast Asia.
In some cases, the threat actors restricted access to the exfiltrated data to only Internet Protocol (IP) addresses originating from Xiamen, China, indicating a possible effort to limit exposure or facilitate localized data handling.
The advisory underscores the prolonged and widespread nature of these cyber operations, highlighting the integration of legitimate-seeming cybersecurity tools into state-sponsored espionage campaigns targeting critical sectors across multiple continents.
Source: SecurityWeek